SECURITY
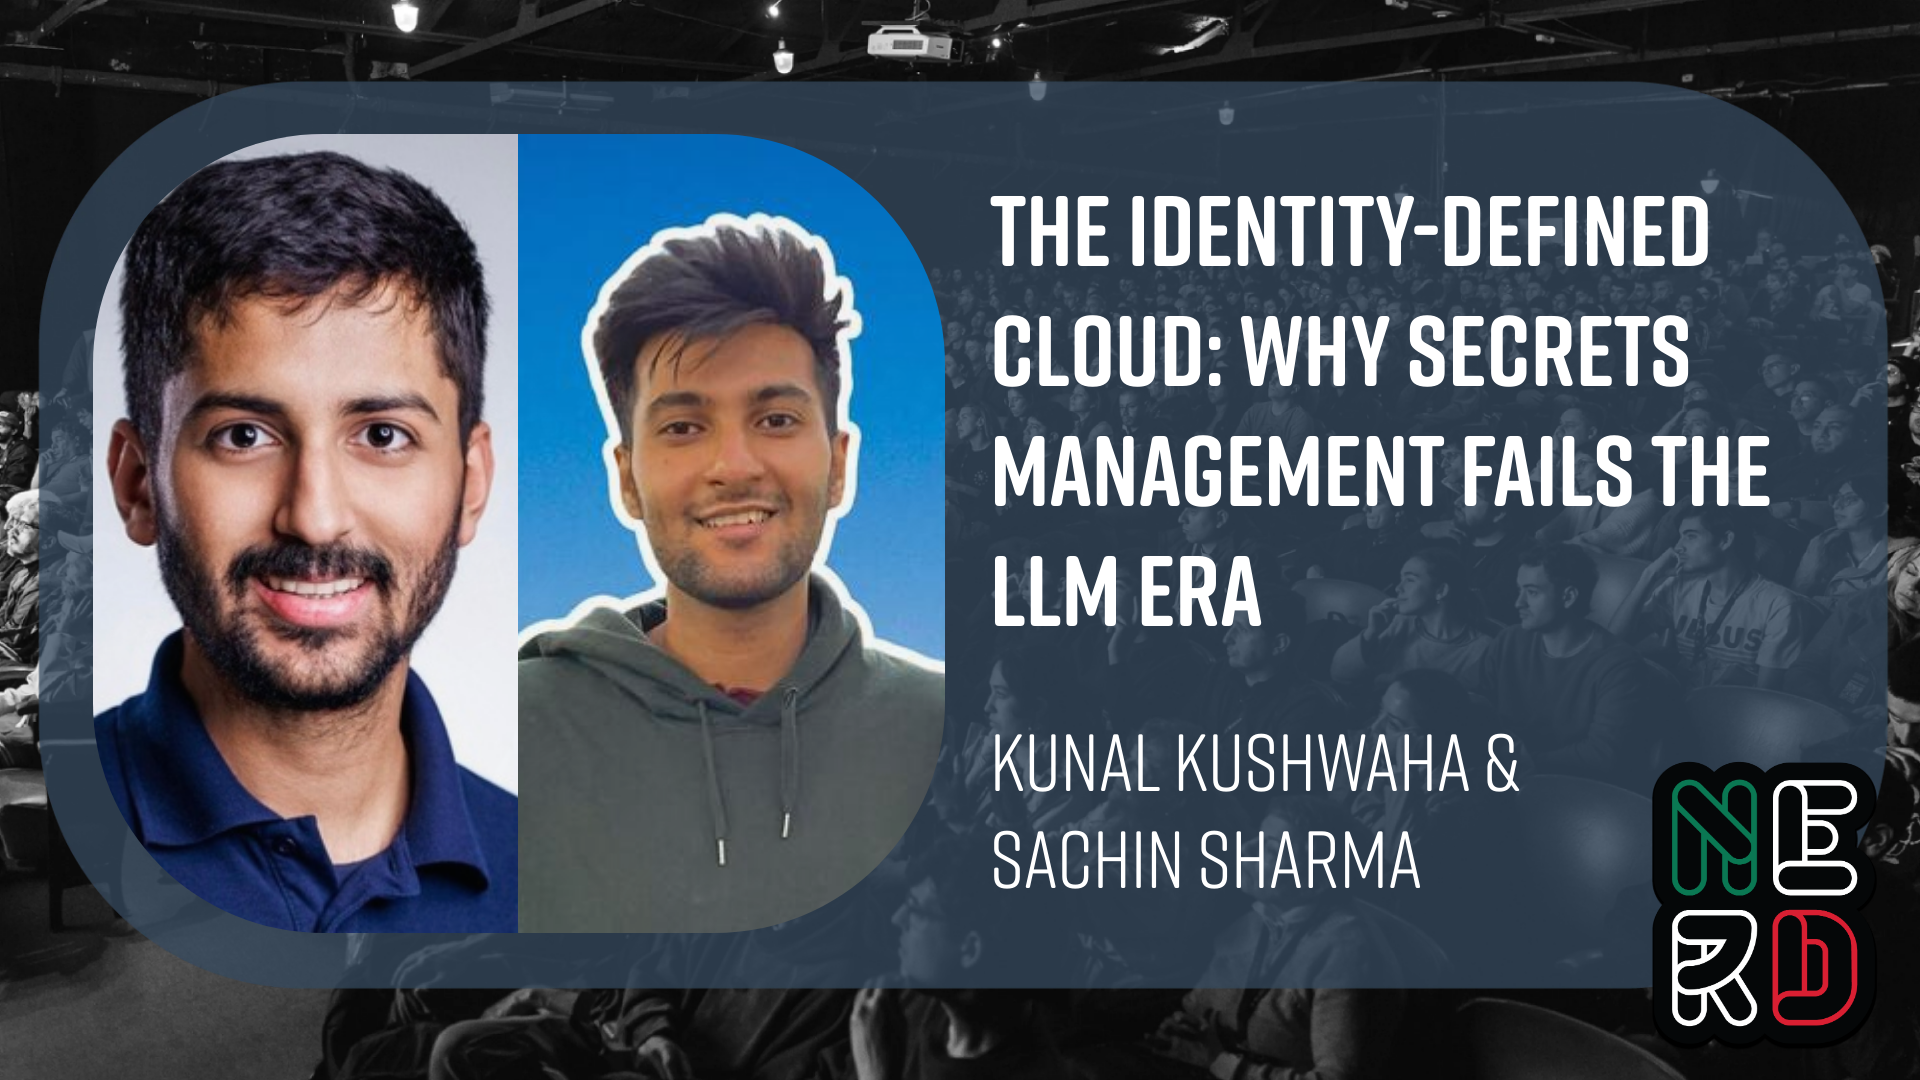
The Identity-Defined Cloud: Why Secrets Management Fails the LLM Era
Leaked credentials continue to be one of the most common and costly security vectors in cloud-native systems, a vulnerability severely amplified by the rise of AI. Traditional secrets management tools help, but they fall short in dynamic environments where LLM applications, autonomous agents, and RAG pipelines require continuous, automated access to sensitive data stores. As these AI workloads scale, identity has officially replaced the network as the true perimeter.
This session will explore how emerging standards like SPIFFE and SPIRE, alongside workload identity and short-lived credentials, are shifting the paradigm from static secret-sharing to cryptographic identity. We will focus heavily on the unique challenges of AI agent authentication, ensuring that autonomous systems have the precise, time-bound permissions they need without risking hardcoded API keys.
Attendees will walk away understanding how these identity patterns eliminate the risk of leaked credentials across complex AI and CI/CD pipelines. The discussion will provide practical strategies for securing data access for LLM agents operating autonomously in production, ultimately showing how to build a zero-trust infrastructure prepared for a future of machine-to-machine, AI-driven operations.
Regístrate para ver la charla de Kunal Kushwaha y Sachin Sharma
Regístrate gratisMás de SECURITY
14:00 - 14:40
Identidad Post-Cuántica: Cómo el IAM se está preparando para la Era Cuántica
 Joao Kuntz
Compromised X-ray: Hacking Medical Equipment
 Arnold Morales
Human vs AI: construyendo y rompiendo una aplicación creada por IA
 Hector Martinez
 Verónica Rivera
¿Qué trae esta receta? Auditando skills de IA con SkillSpector
 Andrea Arredondo
 Matias Muñoz